

Supply Chain Attack
01 Oct 2026

7 min read

When the Model File Becomes the Attack Surface
A look at the Ollama vulnerability and why AI security must protect not just model artifacts, but the software that parses, transforms, and distributes them.
A Curated Collection of Writings, Research, and Solutions
FEATURED ARTICLES
A look at the Ollama vulnerability and why AI security must protect not just model artifacts, but the software that parses, transforms, and distributes them.
A look at the Ollama vulnerability and why AI security must protect not just model artifacts, but the software that parses, transforms, and distributes them.
ChainDrop had valid provenance. MemTensor bypassed install-script controls. Learn what these attacks reveal about verifying package behavior and release history
Know the five software supply chain attack vectors and how vulnerable packages, malicious code, fake packages, altered artifacts, and compromised suppliers can reach your enviornment
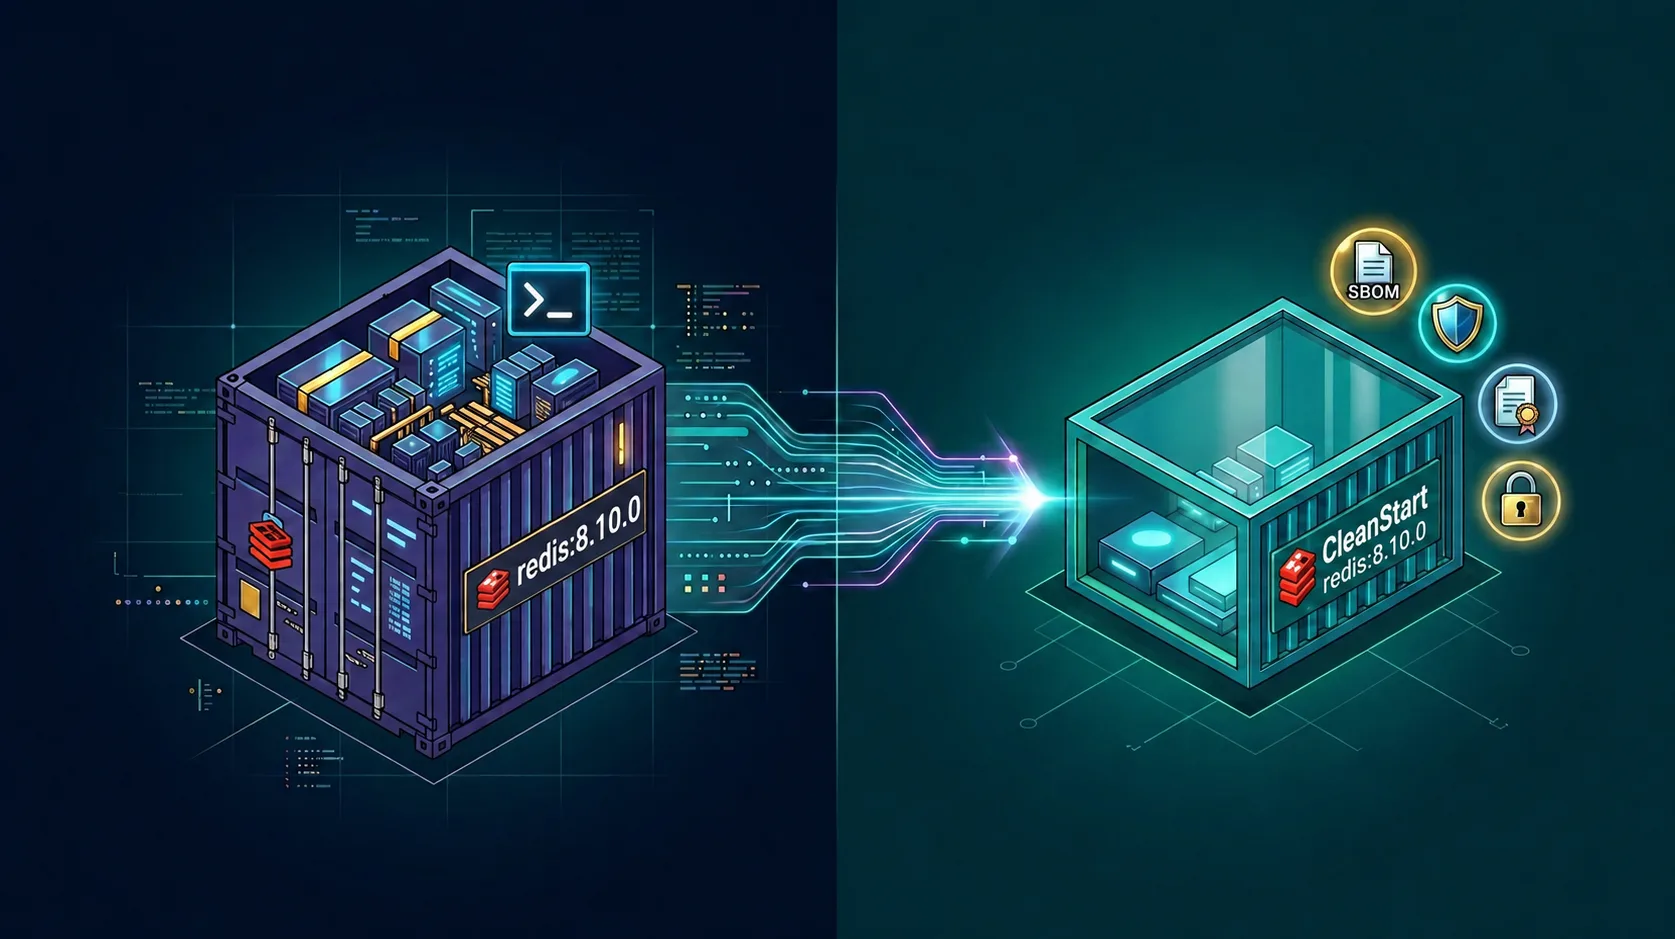
Compare official Redis Docker image with CleanStart Redis. See image size, packages, executables, CVEs, SBOMs, provenance, & more in this technical comparison.
Minimus is shutting down. Learn what to look for in a hardened container image provider and why verified software artifacts matter for your next foundation.
Docker Hardened Images are now available for free, but secure container delivery requires more than image access. Learn what enterprises should evaluate around verification, maintenance, compliance, and trust.
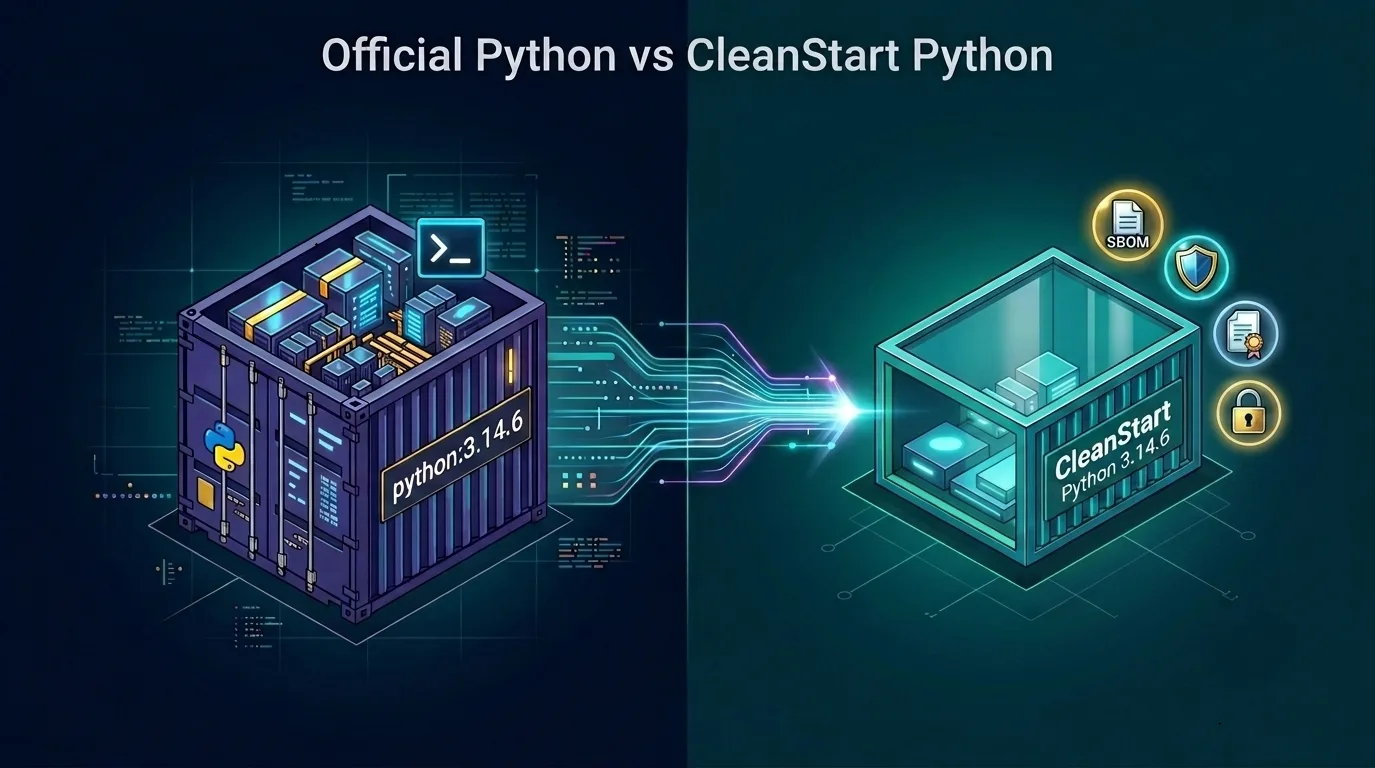
Compare official Python Docker image with CleanStart Python. See image size, packages, executables, CVEs, SBOMs, provenance, & more in this technical comparison.
The LiteLLM supply chain attack shows why vulnerability scanning is not enough. Learn how verified software artifacts strengthen AI software security.

Understand the EU Cyber Resilience Act reporting requirements, including what triggers reporting, the 24-hour and 72-hour deadlines, who must report, and how to prepare for 11 September 2026.
