

Attackers don’t need zero-days to break into modern systems, but instead rely on the steady stream of known flaws that ride along in open-source libraries and container images.

Press Release
November 17, 2026

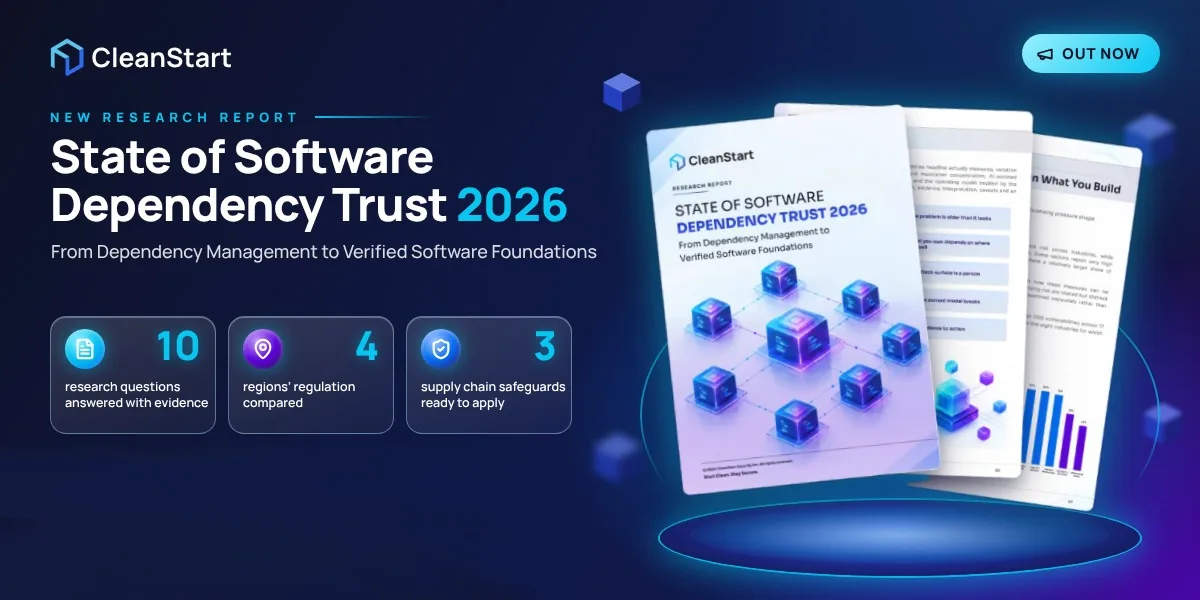
CleanStart Releases State of Software Dependency Trust 2026 Report
Industry-wide report examines how aging components, upstream attacks and AI-assisted development are exposing gaps in software supply chain security


