

As cyberattacks evolve from targeting applications to weaponizing the very pipelines that build them, software supply chain security has become the new front line of enterprise defense. The recent NPM and Shai Hulud incidents have shattered the illusion of safety within trusted repositories, exposing how easily attackers can exploit blind trust in open-source ecosystems.

Press Release
November 17, 2026

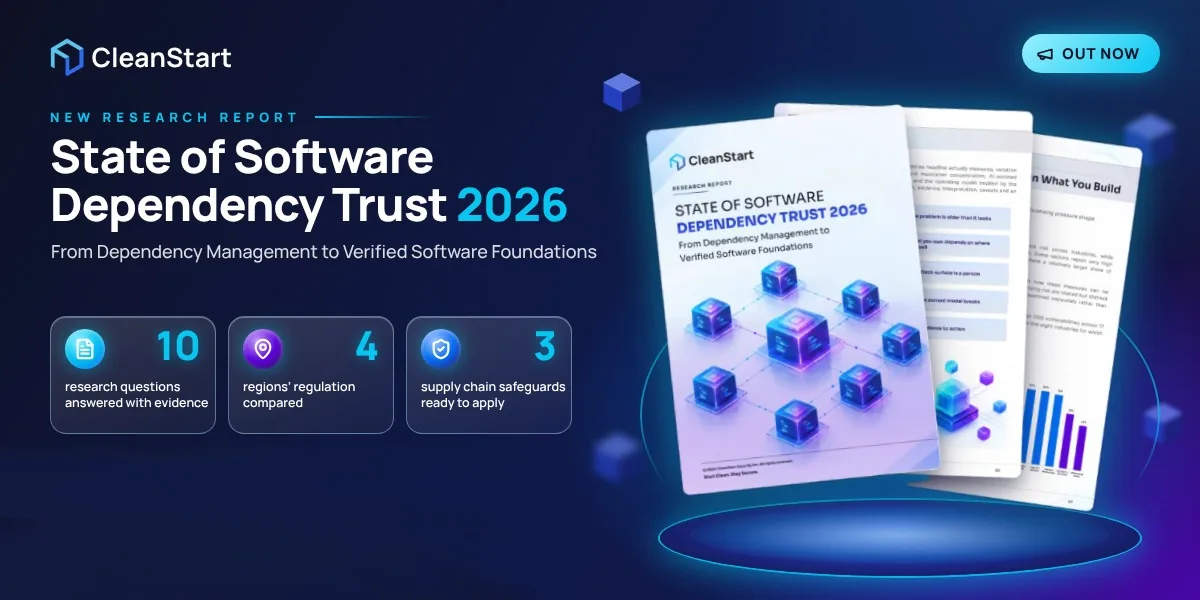
CleanStart Releases State of Software Dependency Trust 2026 Report
Industry-wide report examines how aging components, upstream attacks and AI-assisted development are exposing gaps in software supply chain security


