

A software bill of materials (SBOMs) has been touted as a critical tool in solving software supply-chain security issues, but the rapid change of software ecosystems and the complexity of creating an end-to-end verified chain of code continue to foil widespread adoption.

Press Release
November 17, 2026

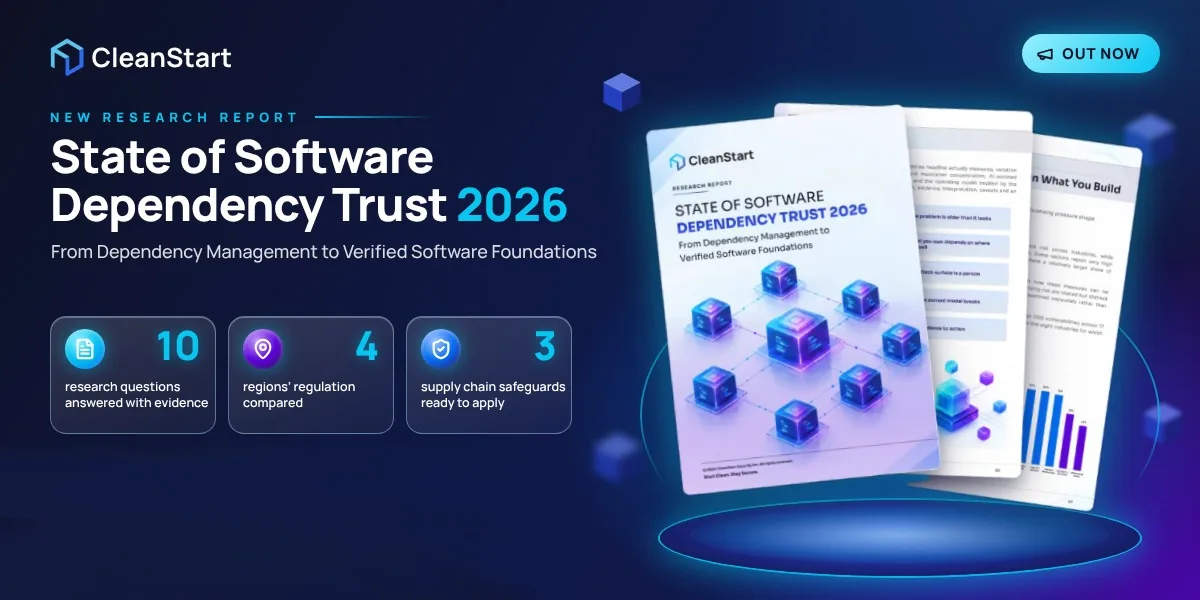
CleanStart Releases State of Software Dependency Trust 2026 Report
Industry-wide report examines how aging components, upstream attacks and AI-assisted development are exposing gaps in software supply chain security


