

A large enterprise recently detected unusual activity across its internal systems. Investigation revealed the source was not a direct attack on the company’s defenses, but a compromise in a widely used third-party software component embedded in critical applications.

Press Release
November 17, 2026

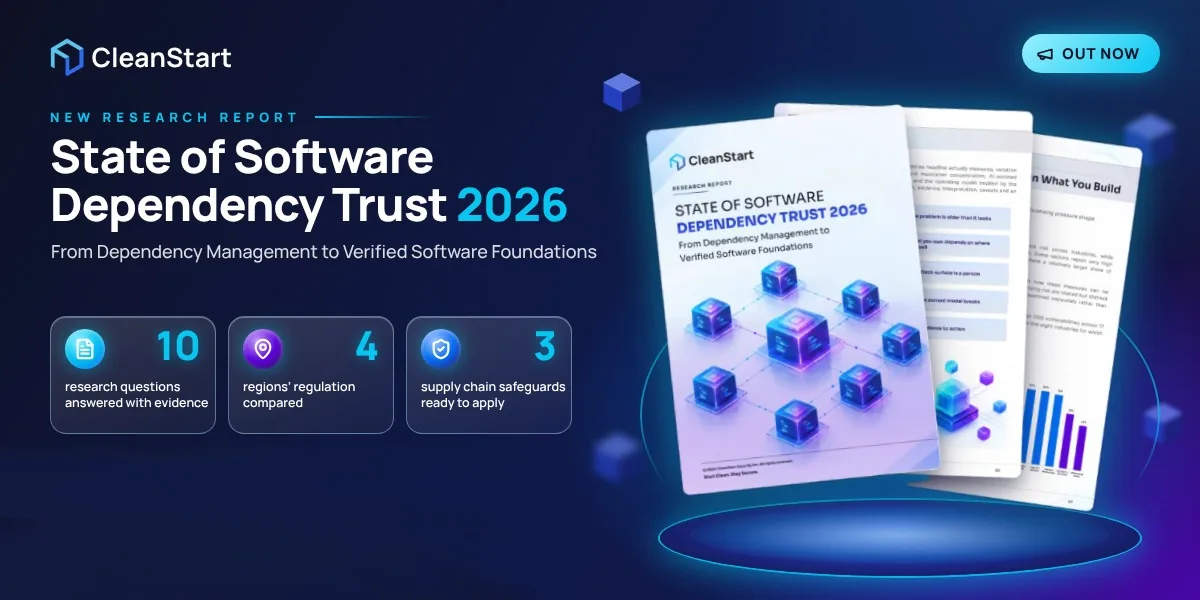
CleanStart Releases State of Software Dependency Trust 2026 Report
Industry-wide report examines how aging components, upstream attacks and AI-assisted development are exposing gaps in software supply chain security


