
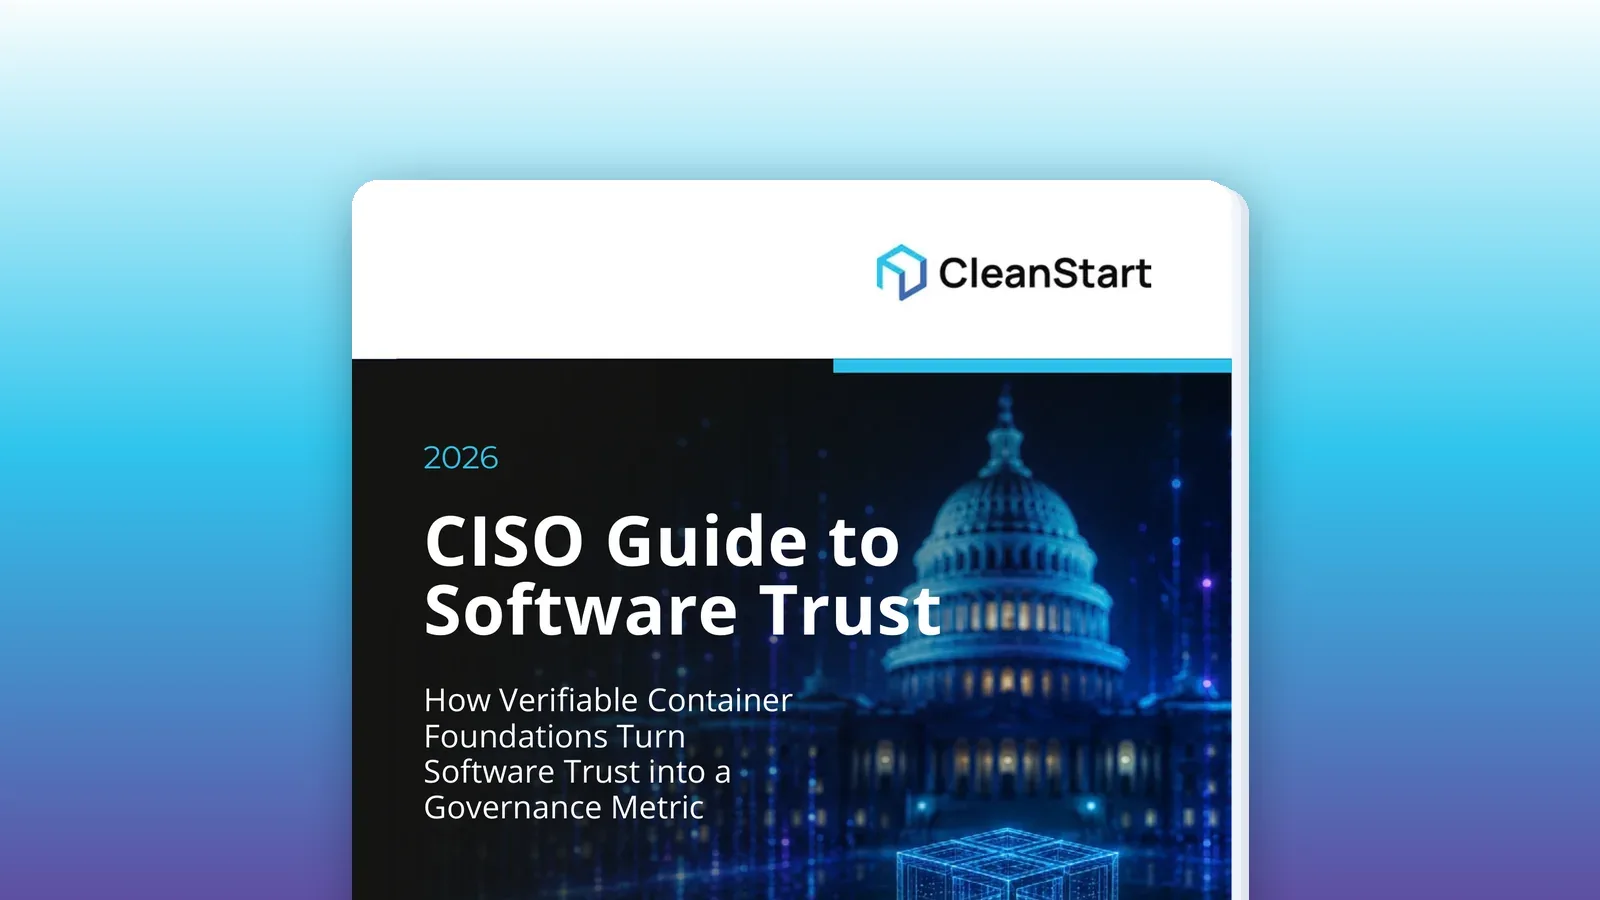
Boards now expect evidence that code was trustworthy before deployment, not merely scanned and patched after release. Published with Cybersecurity Insiders, this guide shows CISOs how to turn that expectation into an operating model built on verified container foundations, codified compliance and measurable trust outcomes.
What's inside
- Why inherited risk is now a governance issue, and why post-deployment patching cannot resolve risk that was inherited at the source.
- A trust maturity model for moving from reactive patching to preventive and provable trust.
- Six imperatives for operationalizing provable trust, from eliminating inherited risk at the source to generating compliance evidence at build time.
- How the model aligns with EO 14028, NIST 800-53 and 800-171, FedRAMP, FIPS 140-2/3, DoD STIGs and the EU Cyber Resilience Act.
- A 100-day blueprint from pilot to proof, and the board-level metrics that show software trust is working.