Product demo2:39
Clean Libraries: Secure Software Dependencies at the Source
About this video
Every release introduces hundreds of dependencies, including transitive packages and AI-generated libraries. Without verification, untrusted components become part of your software supply chain.
Clean Libraries verifies every dependency against security, provenance, and organizational policy before it enters production, ensuring only trusted and clean libraries move forward.
With inline decisions inside the developer workflow, signed attestations for every approval, and CI/CD enforcement, Clean Library ensures only trusted dependencies move forward.
Know what enters production. Secure every release.
Learn more about Clean Libraries: Verify Every Dependency Across Your Workflows : https://clnstrt.co/clnlib
Follow us on our Linkedin Channel for other interesting updates: https://in.linkedin.com/company/cleanstart-official
More videos
Product demo3:08
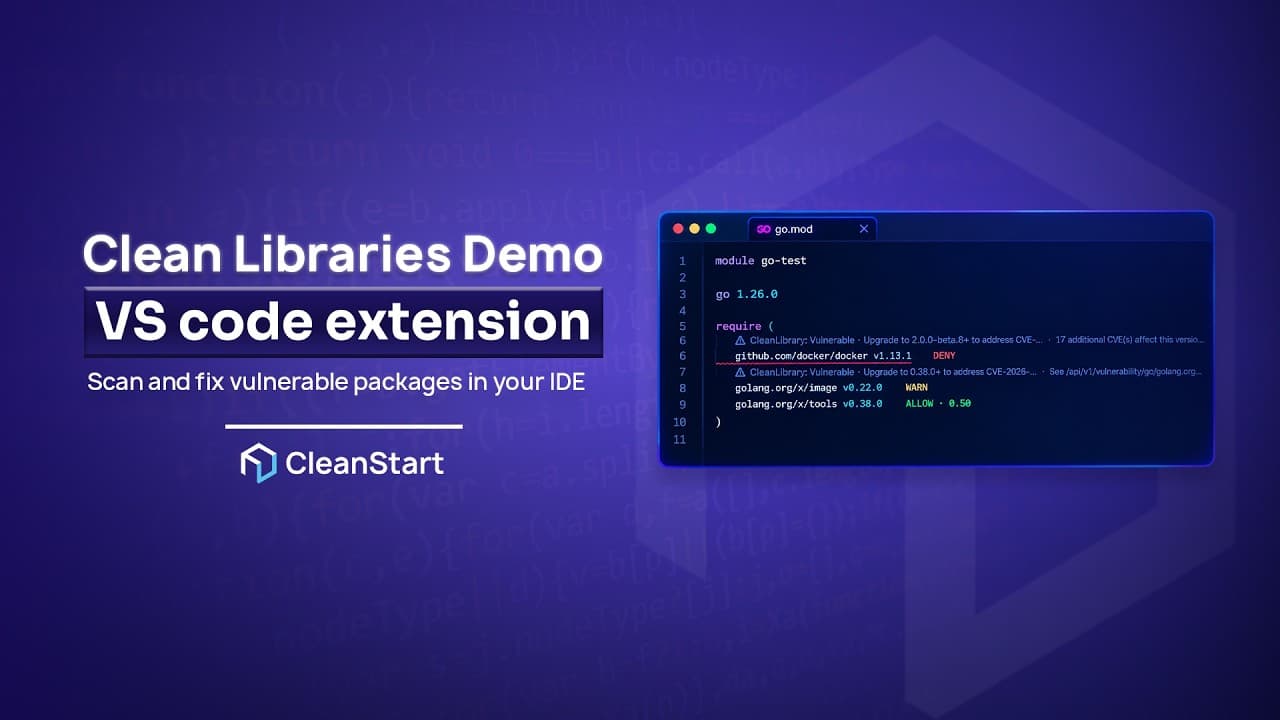
Clean Libraries Demo: Scan and Fix Vulnerabilities in Your IDE
Product demo1:45
Meet CUBR, Your Guide to Trusted Software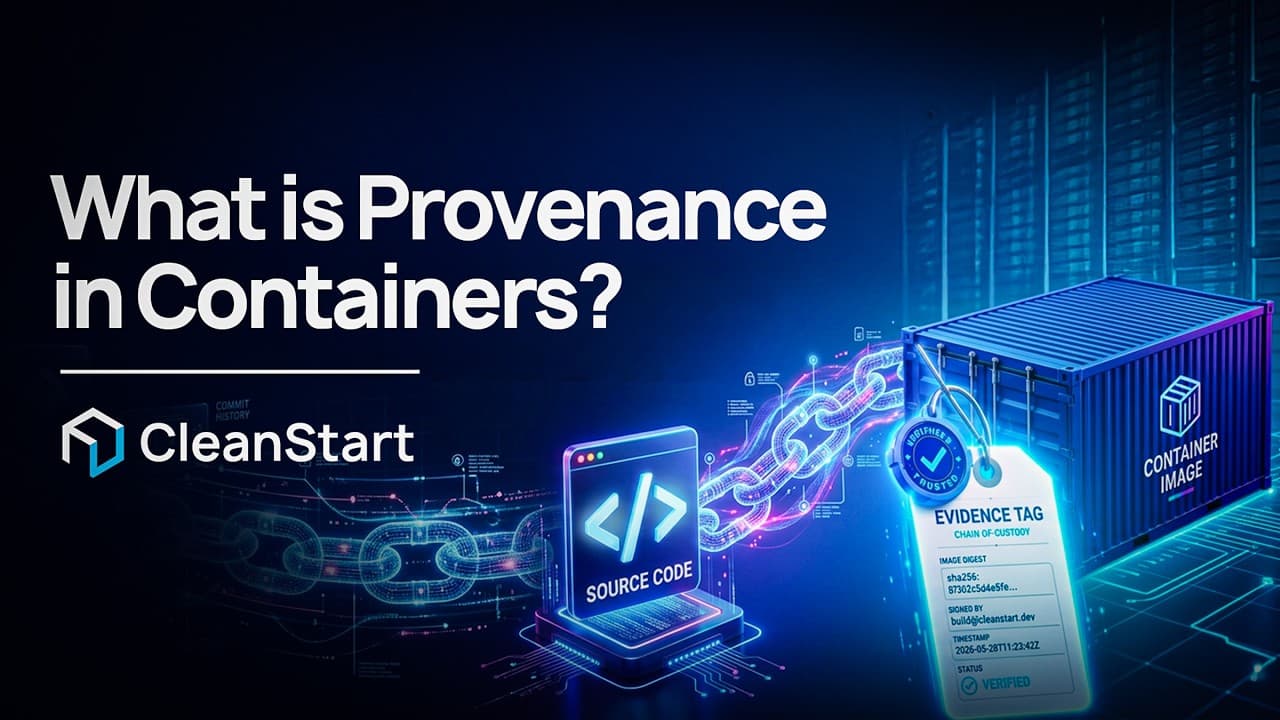
Explainer1:29
What Is Provenance in Containers?
Product demo1:13
CleanSight: Complete Software Security Posture Management
Video
Who Secures Your AI Code? The Hidden Risk in AI-Generated Dependencies.
Video
Clean Libraries MCP: scan and fix vulnerabilities via prompts