Video
Who Secures Your AI Code? The Hidden Risk in AI-Generated Dependencies.
About this video
AI can write code faster than ever. But who checks the dependencies it brings in?
AI coding assistants can introduce vulnerable libraries, look-alike packages, and even malicious dependencies registered under package names that AI tools generate. Without verification, these packages can enter a codebase before security teams have a chance to review them.
In this video, we explore the risks behind AI-generated dependencies, including known vulnerabilities, typosquatting, and slopsquatting, and why dependency security needs to happen before the build.
Meet Clean Libraries by CleanStart.
Clean Libraries verifies dependencies before they enter the build, with three key controls:
🔹 Integrity: Verify packages against the cryptographic hashes of publisher-released artifacts.
🔹 Security verdicts: Assess package versions for known vulnerabilities and malicious-package signals, with signed verdicts for traceability.
🔹 Remediation: Get remediated package versions when the requested version is vulnerable, keeping unsafe dependencies out of the build.
AI can write the code. You still need to trust what it pulls in.
Explore Clean Libraries and verify dependencies before you build.
👉 Learn more: https://www.cleanstart.com/clean-libraries
#AI Security #SoftwareSupplyChainSecurity #DependencySecurity #CleanStart
More videos
Video
Clean Libraries MCP: scan and fix vulnerabilities via prompts
Explainer1:41
What Is VEX? How It Tells Which Vulnerabilities Matter
Explainer1:53
SBOMs Explained: What They Tell You and What They Don’t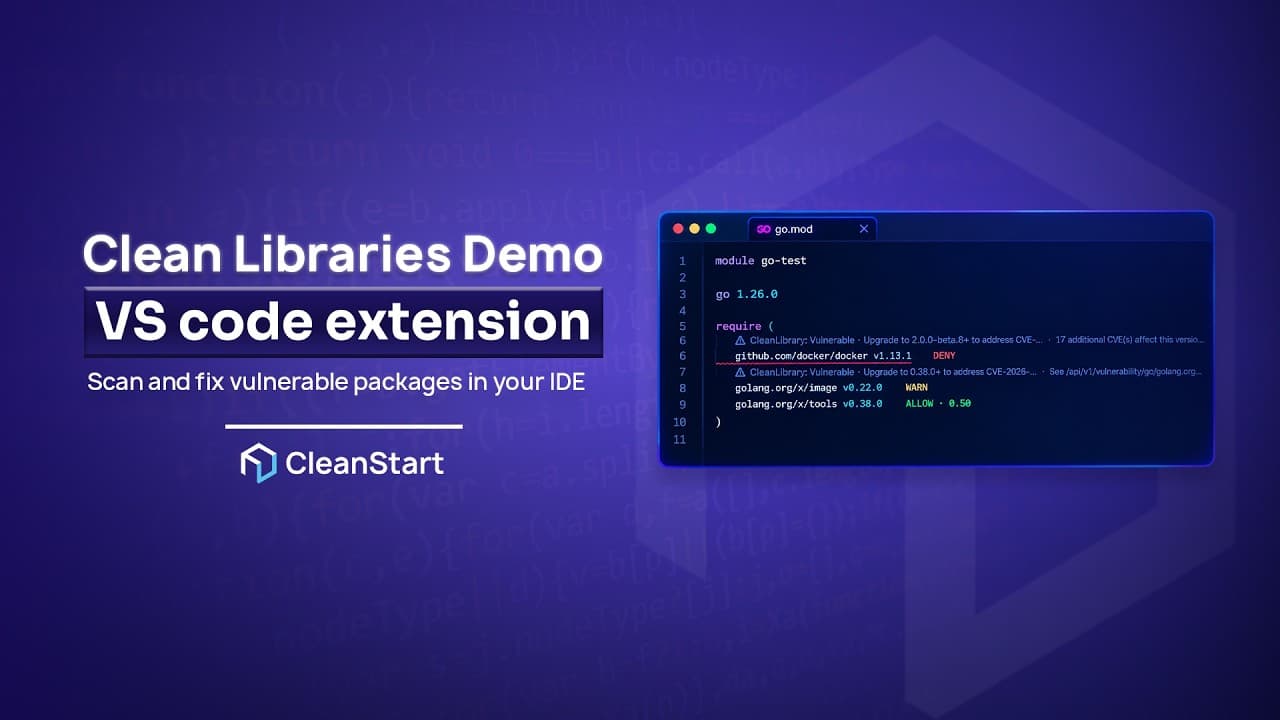
Product demo3:08
Clean Libraries Demo: Scan and Fix Vulnerabilities in Your IDE
Video
Software Supply Chain Security in Age of AI Era
Explainer1:38
What Is Container Sprawl?