Explainer1:41
What Is VEX? How It Tells Which Vulnerabilities Matter
About this video
A vulnerability scanner can flag hundreds of CVEs in a single container image, and some of them can’t be exploited where you run it. VEX (Vulnerability Exploitability eXchange) is how a software supplier tells you which ones apply.
In two minutes, this video covers:
What VEX is and how it pairs with an SBOM
The four statuses: not affected, affected, fixed, and under investigation
Why a “not affected” status must carry a reason, and what that does for your audit trail
Where minimal images fit, by reducing how many vulnerabilities you have to triage in the first place
Explore minimal, source-built container images: https://images.cleanstart.com
More videos
Explainer1:53
SBOMs Explained: What They Tell You and What They Don’t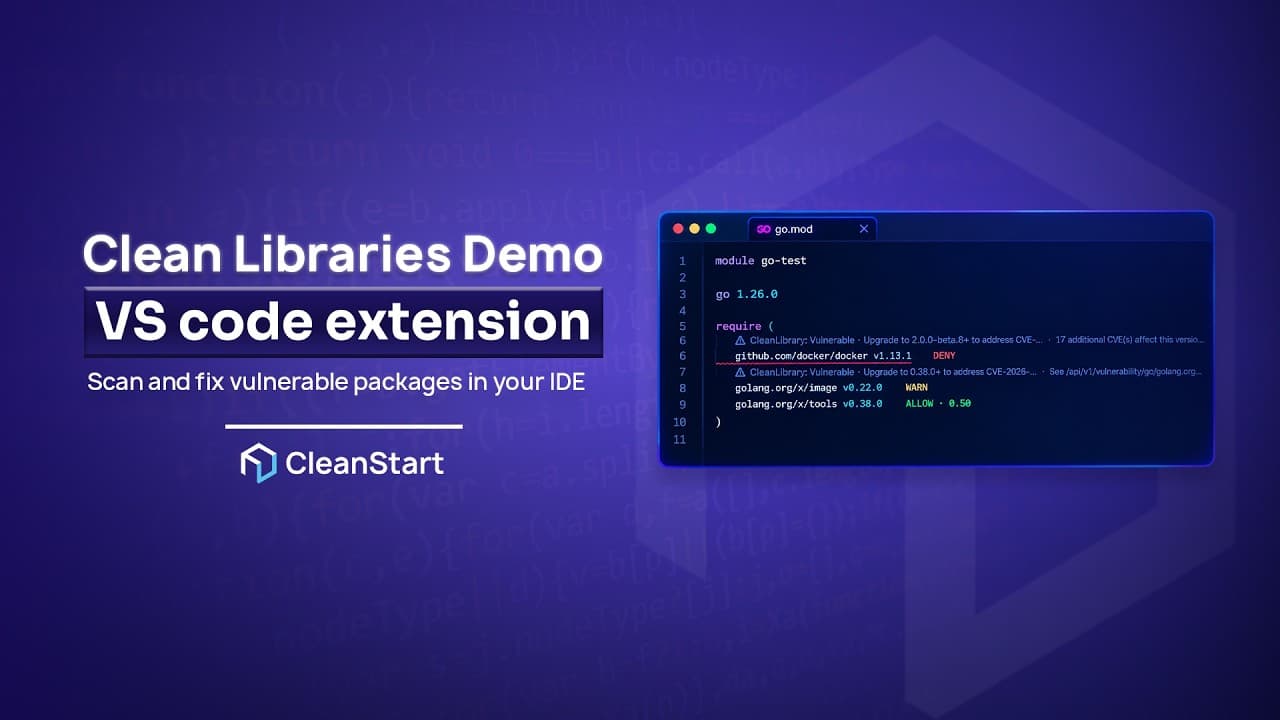
Product demo3:08
Clean Libraries Demo: Scan and Fix Vulnerabilities in Your IDE
Explainer1:29
What Is Provenance in Containers?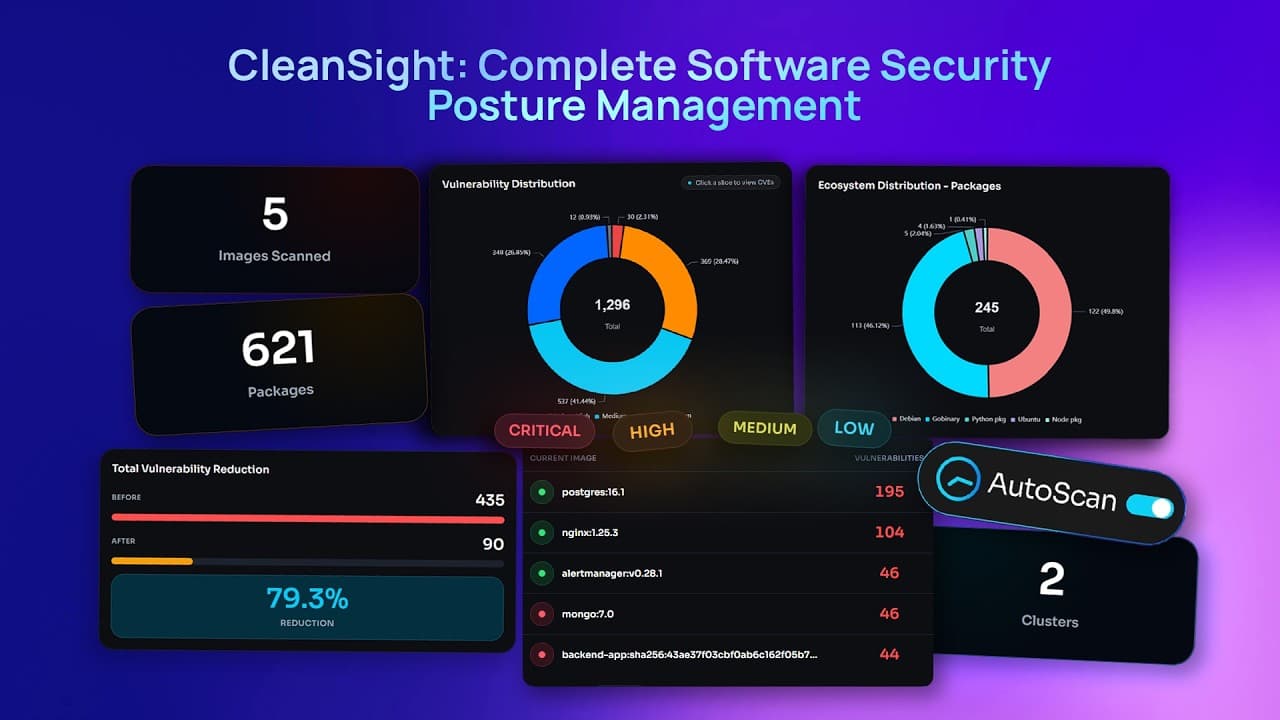
Product demo1:13
CleanSight: Complete Software Security Posture Management
Explainer2:34
CVE Fatigue Explained: Why Your Vulnerability Backlog Never Gets Shorter
Explainer1:38
What Is Container Sprawl?