Explainer2:34
CVE Fatigue Explained: Why Your Vulnerability Backlog Never Gets Shorter
About this video
2,000 CVEs flagged. Your team patches, rebuilds, redeploys. Next week: 500 more. The cycle repeats. This video breaks down what CVE fatigue is, where it actually comes from, and how teams escape it.
2,000 CVEs flagged. Your team patches, rebuilds, redeploys. Next week: 500 more. The cycle repeats.
This video breaks down what CVE fatigue is, where it actually comes from, and how teams escape it.
What you'll learn:
→ Why vulnerability counts keep climbing regardless of how hard your team works
→ Where the noise originates: inherited packages in your base image you never chose
→ How reducing your package count from 500 to 50 eliminates the problem at the source
→ Prevention at the foundation level, before the scanner even runs
📄 Whitepaper: How CleanStart reduces container attack surface → https://www.cleanstart.com/resources/dependency-management-attack-surface-reduction
🔔 Subscribe for more on building containers that start clean.
More videos
Explainer1:41
What Is VEX? How It Tells Which Vulnerabilities Matter
Product demo3:08
Clean Libraries Demo: Scan and Fix Vulnerabilities in Your IDE
Explainer2:33
Public vs Hardened vs CleanStart Images
Explainer0:59
Base Images Explained in 60 Seconds
Explainer2:11
What Is a Shell-Less Container? Container Security Decoded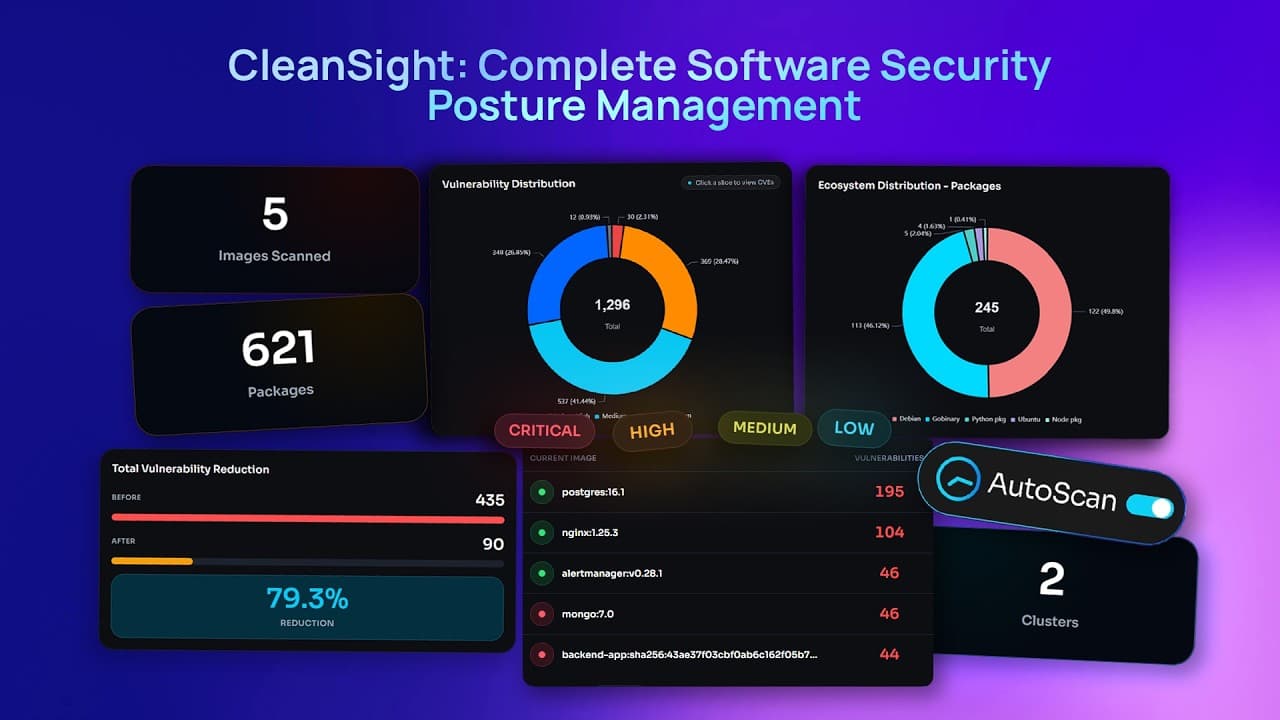
Product demo1:13
CleanSight: Complete Software Security Posture Management