Video
What is Typosquatting Attack and Why AI Development Increases the Risk
About this video
Typosquatting is a software supply chain attack in which attackers publish malicious packages with names that closely resemble legitimate, popular libraries. A single misplaced, missing or extra character can be enough to trick developers or AI coding assistants into installing the wrong dependency.
In this video, we explain how typosquatting works, how malicious packages disguise themselves as legitimate dependencies, and how attackers can execute malicious code during installation to steal credentials, environment variables and source code.
We also explore why AI-assisted development increases the risk of typosquatting. As AI coding assistants introduce more dependencies into projects, malicious packages have more opportunities to enter the software supply chain.
Stop malicious dependencies before they enter your build.
Clean Libraries verifies open-source dependencies by checking their origin, behaviour and equivalence. Suspicious packages can be flagged or blocked based on organisational policies, with signed verdicts providing verifiable evidence of each decision.
Explore Clean Libraries: https://www.cleanstart.com/clean-libraries
More videos
Video
Who Secures Your AI Code? The Hidden Risk in AI-Generated Dependencies.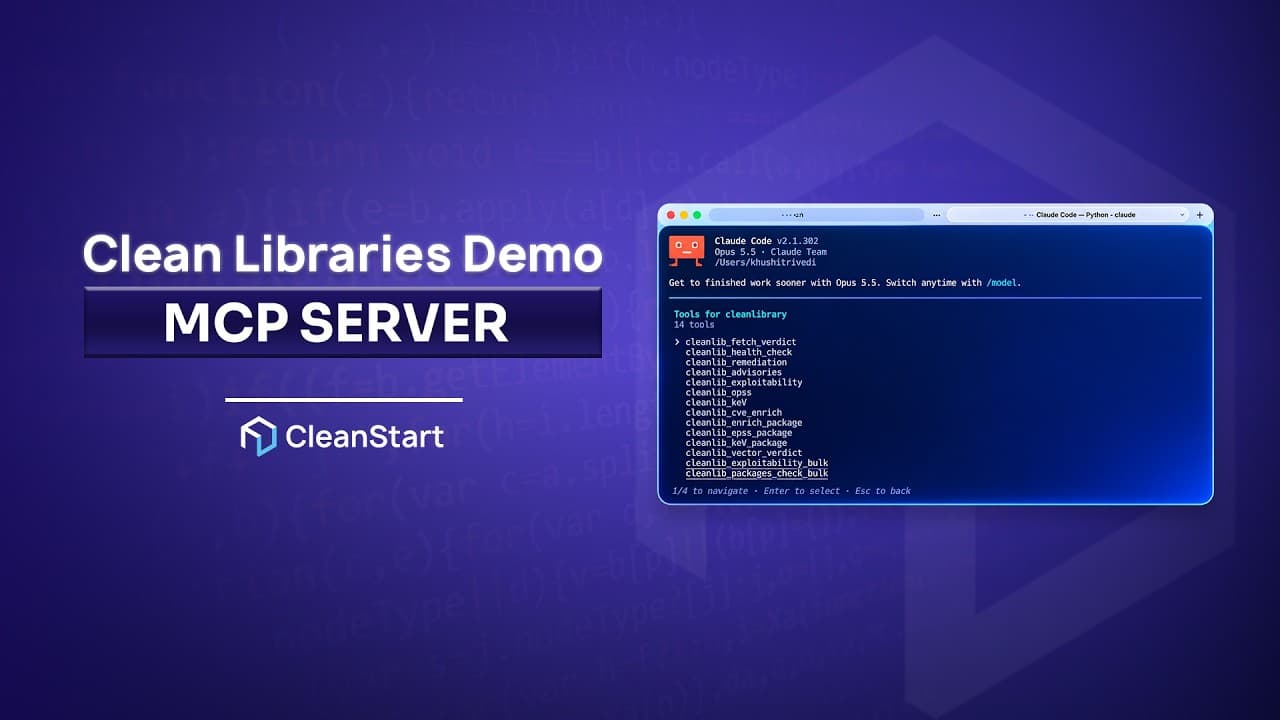
Video
Clean Libraries MCP: scan and fix vulnerabilities via prompts
Explainer1:41
What Is VEX? How It Tells Which Vulnerabilities Matter
Explainer1:53
SBOMs Explained: What They Tell You and What They Don’t
Product demo3:08
Clean Libraries Demo: Scan and Fix Vulnerabilities in Your IDE
Video
Software Supply Chain Security in Age of AI Era