

27 Aug 2026

6 min read

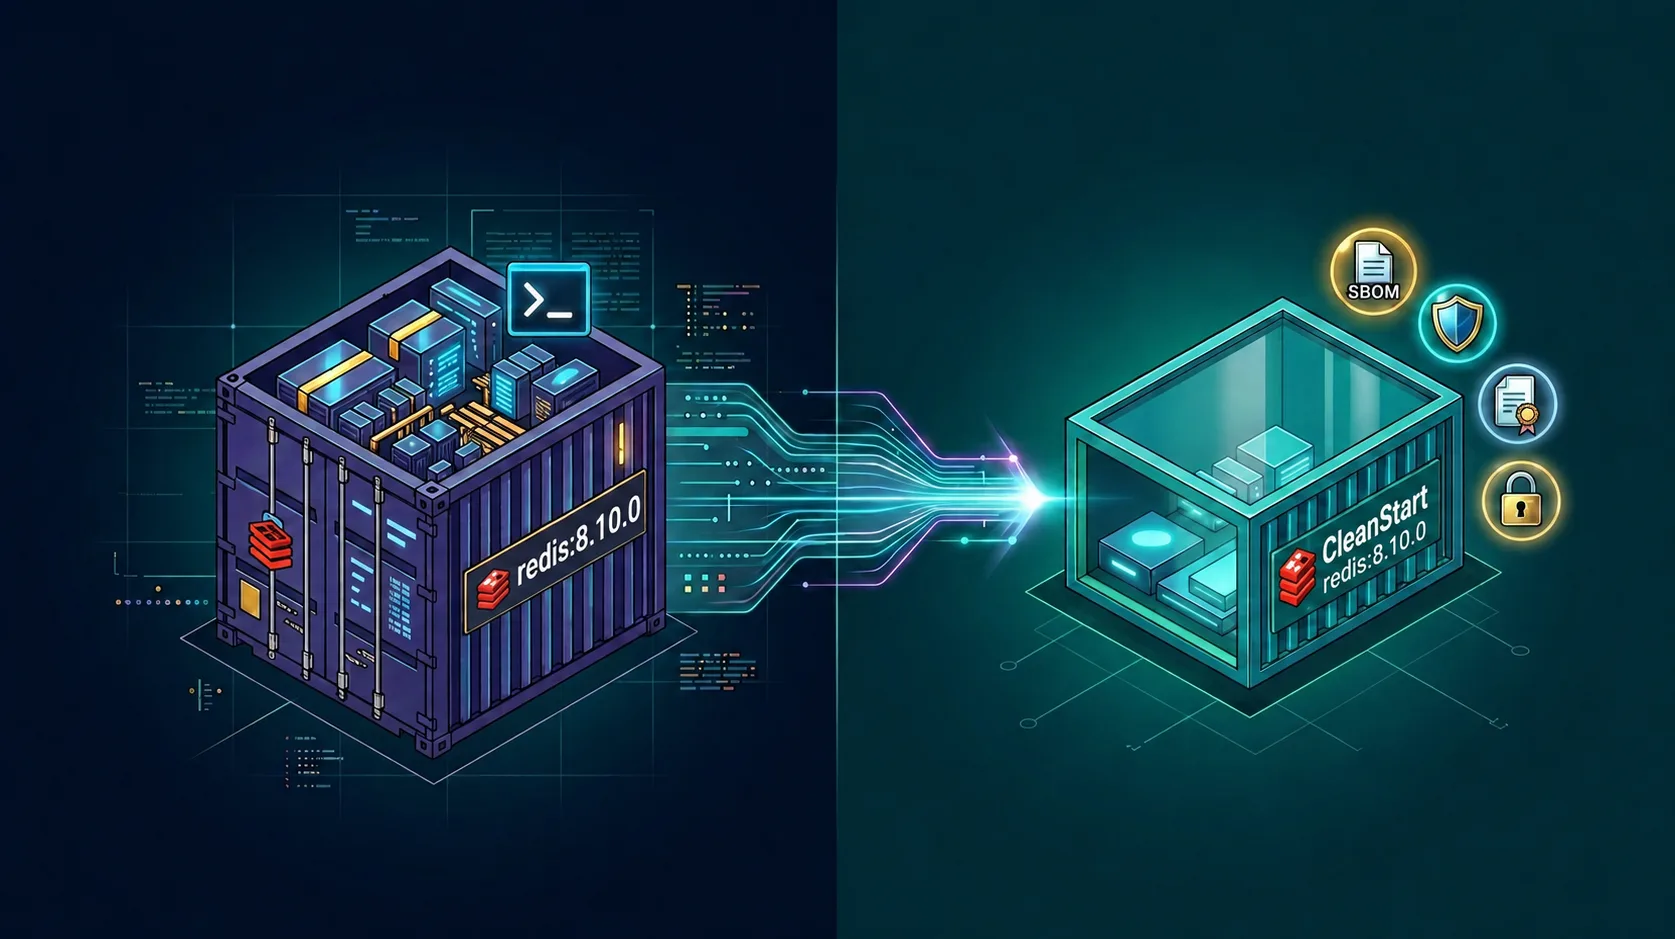
Official Redis Docker Image vs CleanStart Redis Image
Compare official Redis Docker image with CleanStart Redis. See image size, packages, executables, CVEs, SBOMs, provenance, & more in this technical comparison.
A Curated Collection of Writings, Research, and Solutions
FEATURED ARTICLES
Compare official Redis Docker image with CleanStart Redis. See image size, packages, executables, CVEs, SBOMs, provenance, & more in this technical comparison.
Compare official Redis Docker image with CleanStart Redis. See image size, packages, executables, CVEs, SBOMs, provenance, & more in this technical comparison.
Minimus is shutting down. Learn what to look for in a hardened container image provider and why verified software artifacts matter for your next foundation.
Docker Hardened Images are now available for free, but secure container delivery requires more than image access. Learn what enterprises should evaluate around verification, maintenance, compliance, and trust.
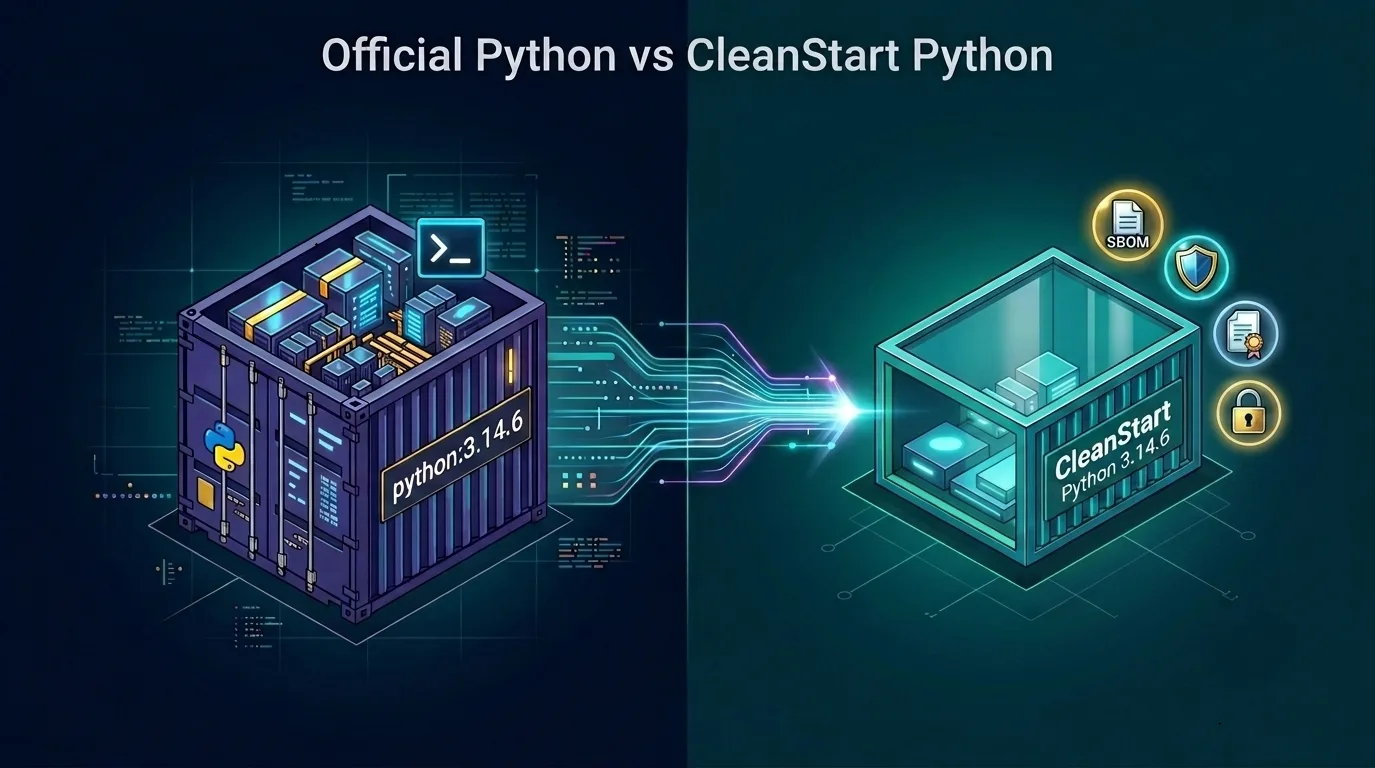
Compare official Python Docker image with CleanStart Python. See image size, packages, executables, CVEs, SBOMs, provenance, & more in this technical comparison.
The LiteLLM supply chain attack shows why vulnerability scanning is not enough. Learn how verified software artifacts strengthen AI software security.

Understand the EU Cyber Resilience Act reporting requirements, including what triggers reporting, the 24-hour and 72-hour deadlines, who must report, and how to prepare for 11 September 2026.
Discover how FakeGit uses 7,600 malicious GitHub repositories to trick AI coding agents into recommending malware, and why dependency governance must start at software discovery
Learn how to migrate from Alpine or Debian to hardened container base images, including image mapping, Dockerfile changes, staged rollout, validation, and enforcement.
Learn the differences between distroless, hardened, Alpine, and minimal base images, and how to choose the right container image for security, size, and compliance.
